12:47Machine-translated from Azerbaijani by AIRead in Azerbaijani
Apple Patches 9 Vulnerabilities in HomeView Smart Home Device, Including Messages Risk
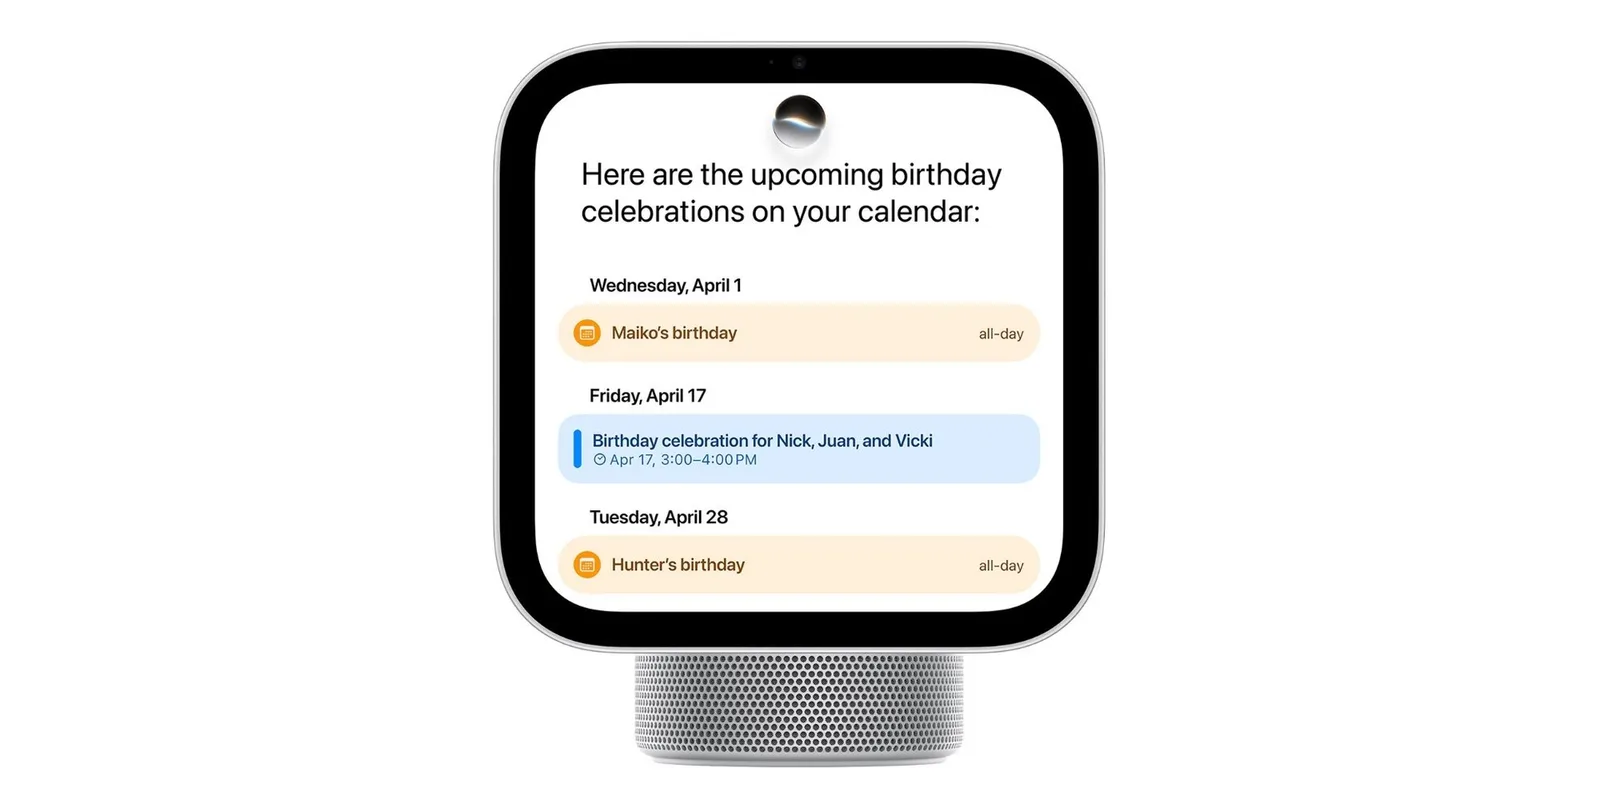
Apple released a security update before the first HomeView devices were delivered to customers on November 13. The update, released on November 12, fixes 9 security vulnerabilities. Because these vulnerabilities have already been publicly disclosed, device owners are advised to install version 27.2 immediately. This is the first system update released for HomeView.
The build number for the HomeView Software 27.2 update is 24V526. One of the most serious vulnerabilities could have allowed a remote attacker to join an iMessage group and read the conversations. Another flaw could have allowed a malicious Bluetooth device to connect without the user’s consent. It was also possible to bypass the limit on repeated attempts to enter the AirPlay connection code. The update fixes this issue as well.
Other fixes prevent apps from accessing sensitive user data and eliminate the risk of process memory corruption during a Bluetooth connection. A flaw that caused memory corruption when specially crafted data was processed has also been patched. In addition, code that allowed someone who later joined an iMessage group to view earlier messages has been removed. Repeated attempts by people on the same network to enter AirPlay connection codes have also been restricted.
Apple has also confirmed that another software update for HomeView will be released in December. After that version is released, the AI assistant called Siri will be able to work with security accessories. The assistant currently refuses to unlock a door or open a garage door using a voice command. The company has not disclosed what additional security checks the new feature will include.