12:42Machine-translated from Azerbaijani by AIRead in Azerbaijani
Apple Releases 27.2 Updates Fixing 329 Vulnerabilities
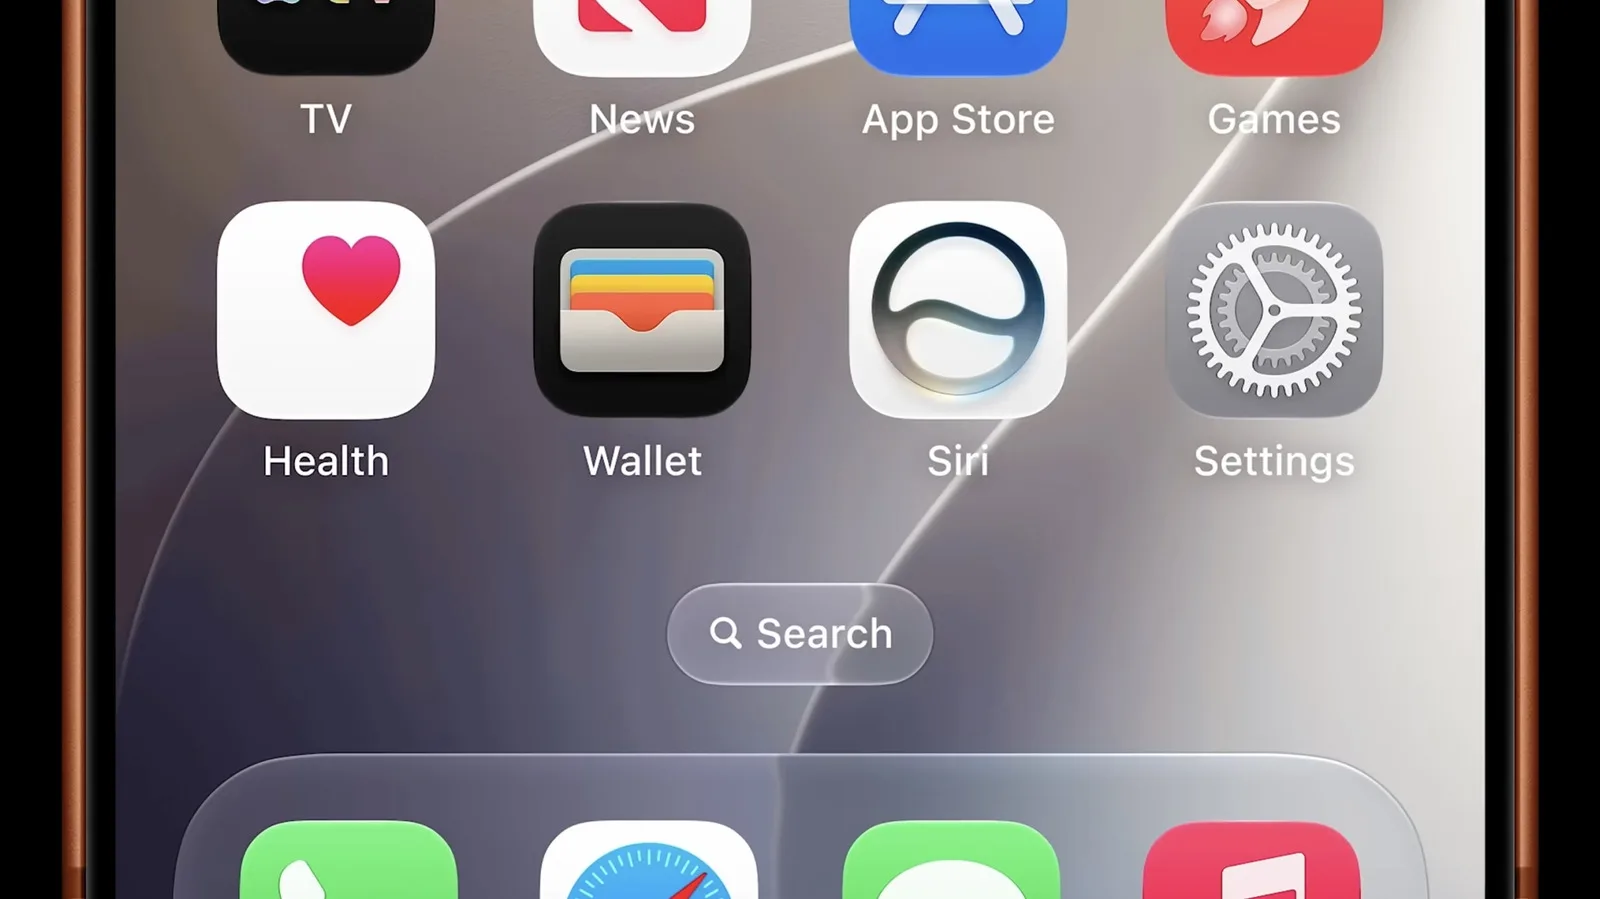
Apple released the 27.2 system updates for its devices on October 27. With this update, the AI-powered Siri AI assistant introduced in iOS 27 last month can do more. Its conversation memory feature allows it to retain useful context from previous conversations. Siri AI now supports French, Japanese, Korean, Portuguese and Spanish. The personal context updates allow Siri AI to consult more sources of information. The assistant can use photos sent in Messages, participant lists in Calendar invitations, voice messages, Safari history and the Reading List. In the Excluded Apps section, users can prevent a specific app from being accessed by Siri, search and suggestions. Users can also select and copy only the part of a response they need. The AI updates work on all iPhone 16 models, newer phones, and the iPhone 15 Pro and iPhone 15 Pro Max. Other iPhone models receive the general updates in iOS 27.2. Users can edit the titles and comments of shared albums in the Photos app. Messages suggests an action based on the text being written. The SynthID feature also helps identify images created or modified with AI. Separate updates have also been prepared for the first foldable iPhone Duo. The phone now supports Apple Pencil. The Edge Light feature creates a ring of light around the edge of the screen during video calls. watchOS 27.2 has also received the same AI updates. According to Apple, Apple Watch delivers responses faster. The updates have also been released for Mac, iPad, Apple TV, Vision Pro and HomePod devices. Apple has fixed 329 unique security vulnerabilities in the new system versions. Because the same vulnerabilities affect multiple systems, the total number of CVE entries has reached 1,265. CVE is a common list in which security issues are recorded. A vulnerability in CoreMedia could have allowed a malicious app to gain unauthorized access to the cameras on iPhone, iPad, Mac and Vision Pro devices. Another issue in Apple Intelligence could have allowed a remote attacker to access sensitive information.
 A separate Siri vulnerability in macOS Tahoe could have allowed apps to access sensitive user data. Several issues were also found in WebKit, the engine used by browsers. A specially crafted website could have exploited these vulnerabilities to execute arbitrary code on a device. Apple has released numerous fixes for WebKit in recent months. The new security advisories separately identify several vulnerabilities found by AI tools and research groups. Earlier this year, the Coruna and DarkSword attack tools exploited WebKit vulnerabilities in older iPhone models. A CoreGraphics fix has also been released for iOS 18 and iPadOS 18. The vulnerability could allow code to be executed on a device through a malicious file. The issue was first fixed last month and may have been exploited in sophisticated attacks against specific individuals on systems older than iOS 27. The number of identified vulnerabilities may increase as the security advisories are updated.
The personal context updates allow Siri AI to consult more sources of information. The assistant can use photos sent in Messages, participant lists in Calendar invitations, voice messages, Safari history and the Reading List. In the Excluded Apps section, users can prevent a specific app from being accessed by Siri, search and suggestions. Users can also select and copy only the part of a response they need. The AI updates work on all iPhone 16 models, newer phones, and the iPhone 15 Pro and iPhone 15 Pro Max. Other iPhone models receive the general updates in iOS 27.2. Users can edit the titles and comments of shared albums in the Photos app. Messages suggests an action based on the text being written. The SynthID feature also helps identify images created or modified with AI. Separate updates have also been prepared for the first foldable iPhone Duo. The phone now supports Apple Pencil. The Edge Light feature creates a ring of light around the edge of the screen during video calls. watchOS 27.2 has also received the same AI updates. According to Apple, Apple Watch delivers responses faster. The updates have also been released for Mac, iPad, Apple TV, Vision Pro and HomePod devices. Apple has fixed 329 unique security vulnerabilities in the new system versions. Because the same vulnerabilities affect multiple systems, the total number of CVE entries has reached 1,265. CVE is a common list in which security issues are recorded. A vulnerability in CoreMedia could have allowed a malicious app to gain unauthorized access to the cameras on iPhone, iPad, Mac and Vision Pro devices. Another issue in Apple Intelligence could have allowed a remote attacker to access sensitive information. A separate Siri vulnerability in macOS Tahoe could have allowed apps to access sensitive user data. Several issues were also found in WebKit, the engine used by browsers. A specially crafted website could have exploited these vulnerabilities to execute arbitrary code on a device. Apple has released numerous fixes for WebKit in recent months. The new security advisories separately identify several vulnerabilities found by AI tools and research groups. Earlier this year, the Coruna and DarkSword attack tools exploited WebKit vulnerabilities in older iPhone models. A CoreGraphics fix has also been released for iOS 18 and iPadOS 18. The vulnerability could allow code to be executed on a device through a malicious file. The issue was first fixed last month and may have been exploited in sophisticated attacks against specific individuals on systems older than iOS 27. The number of identified vulnerabilities may increase as the security advisories are updated.